Evidence you can hand over,not a report you assemble.
Compliance here is a view on what the fleet reports, produced the moment you ask for it.
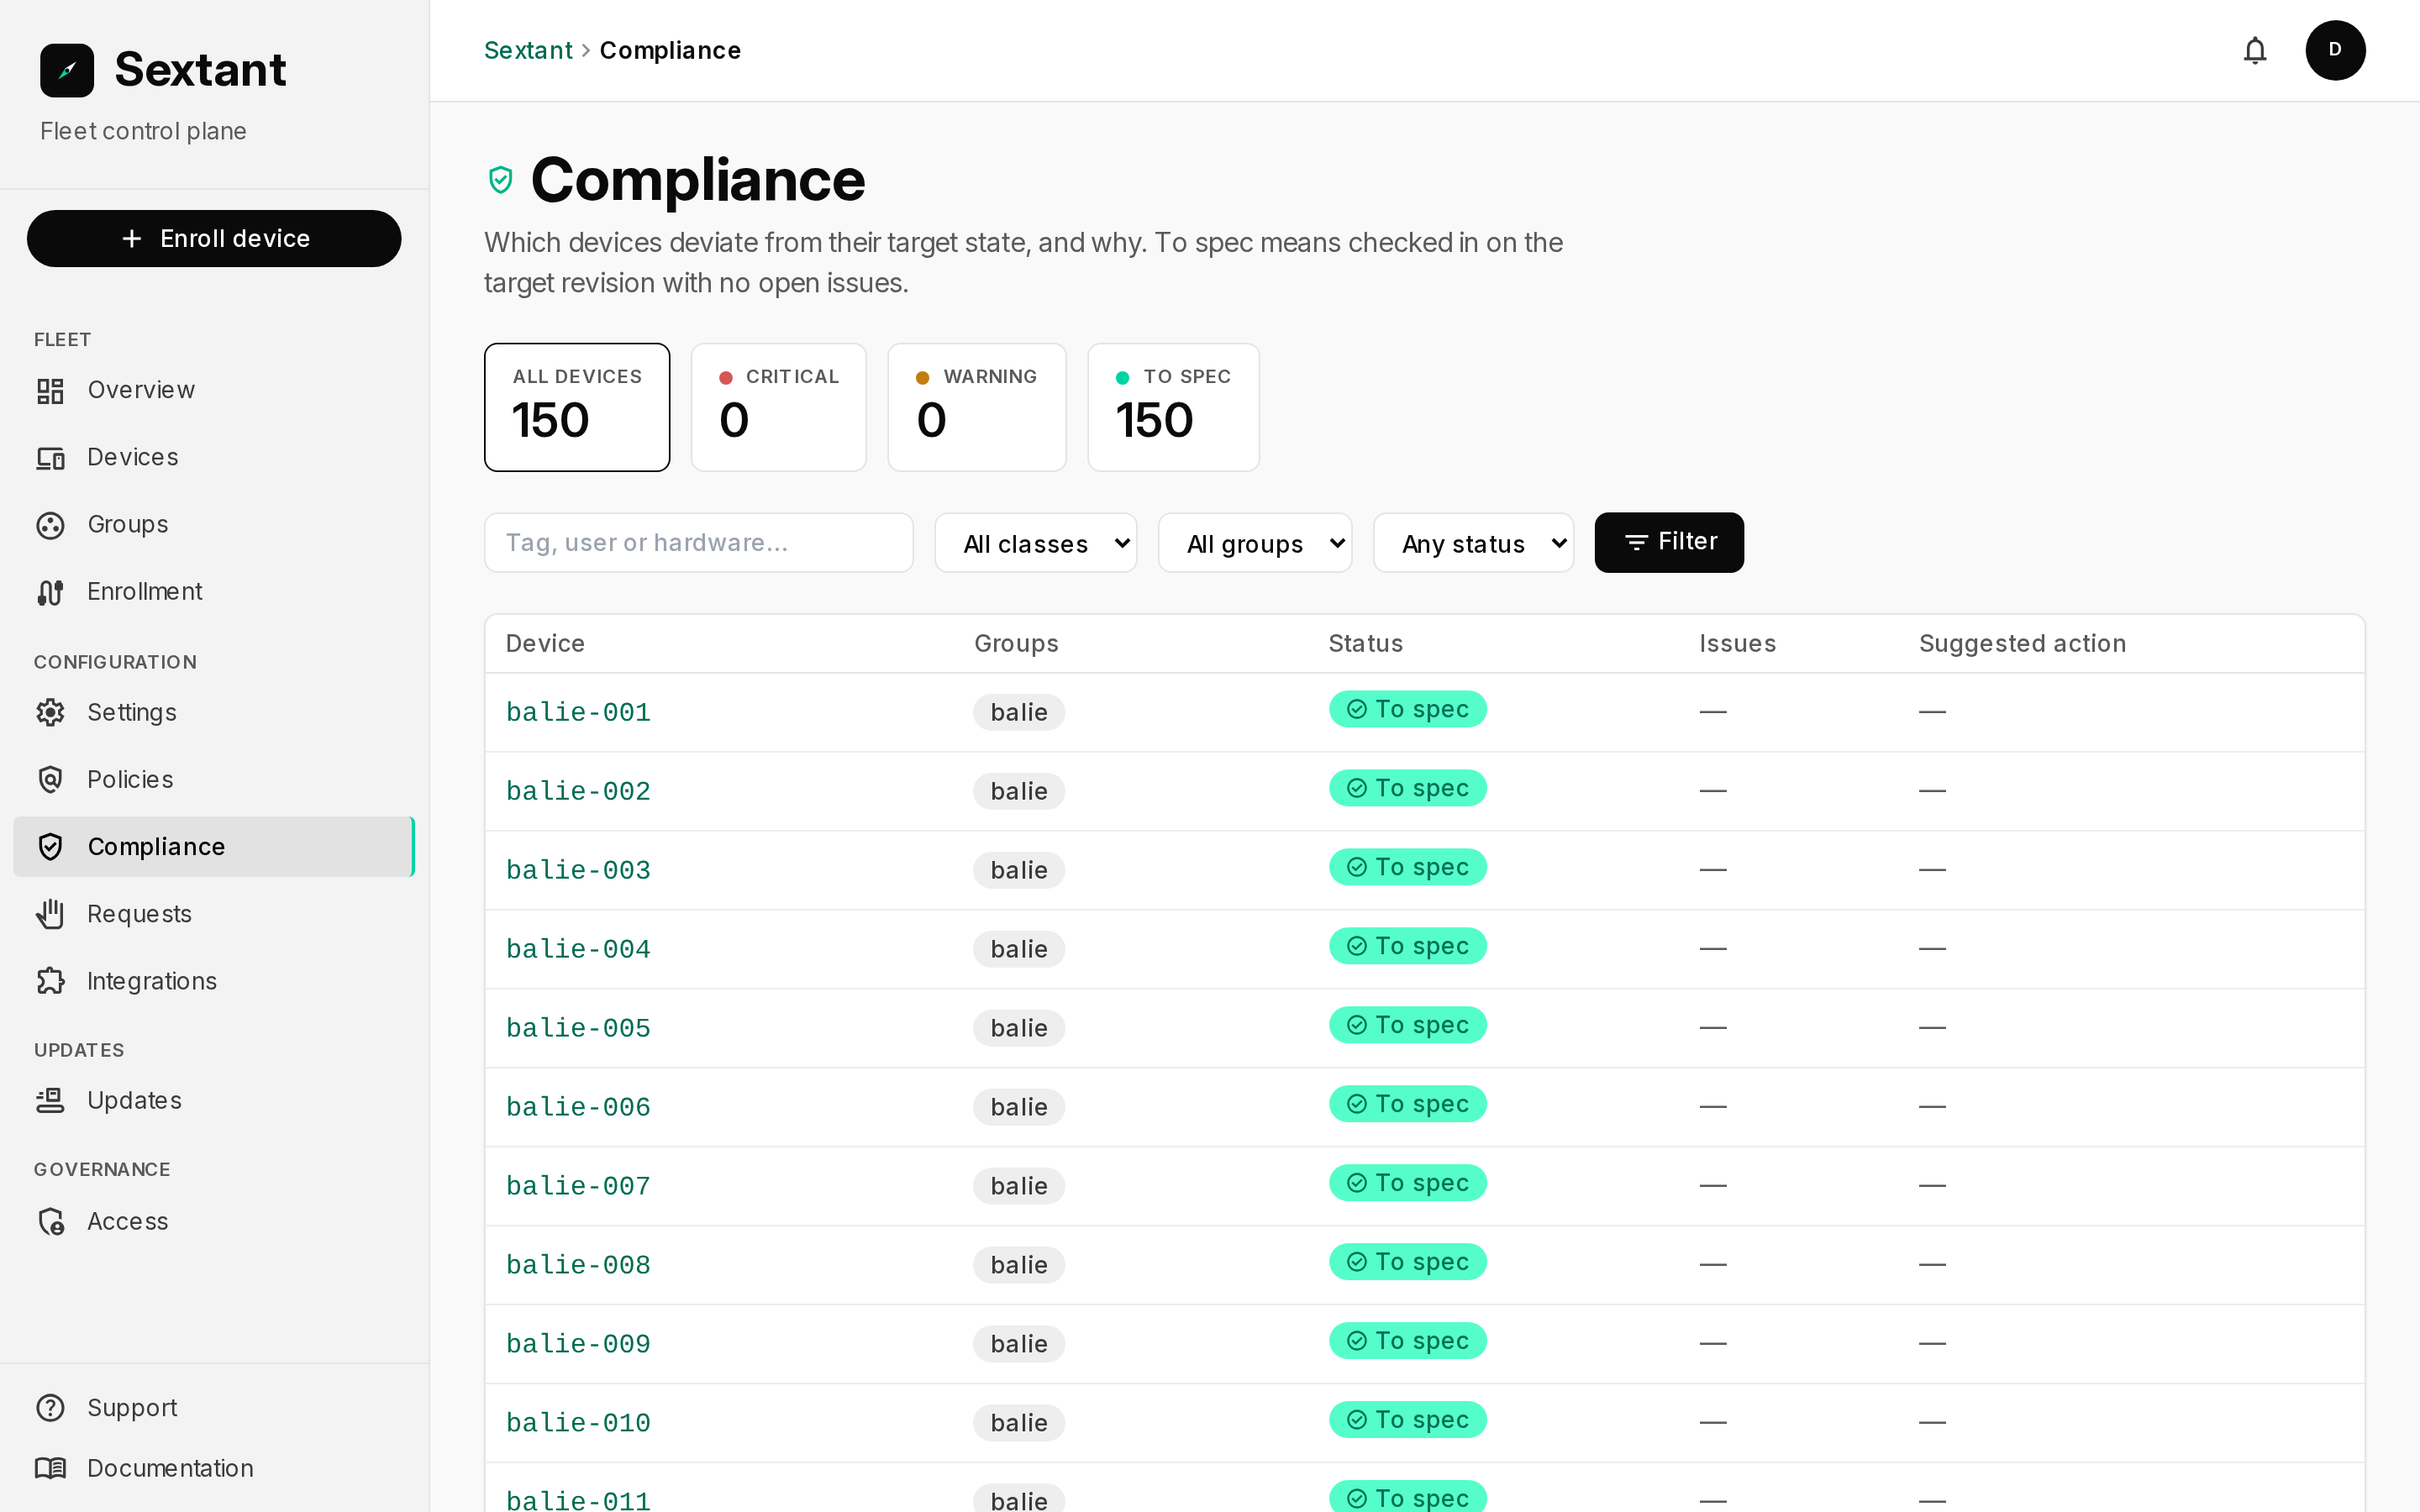
Deviation, with the reason next to it.
Every device is either on the target version with no open issues, or it is not and the console names why. No sampling, no scan window, no spreadsheet that is a week old by the time it is read.
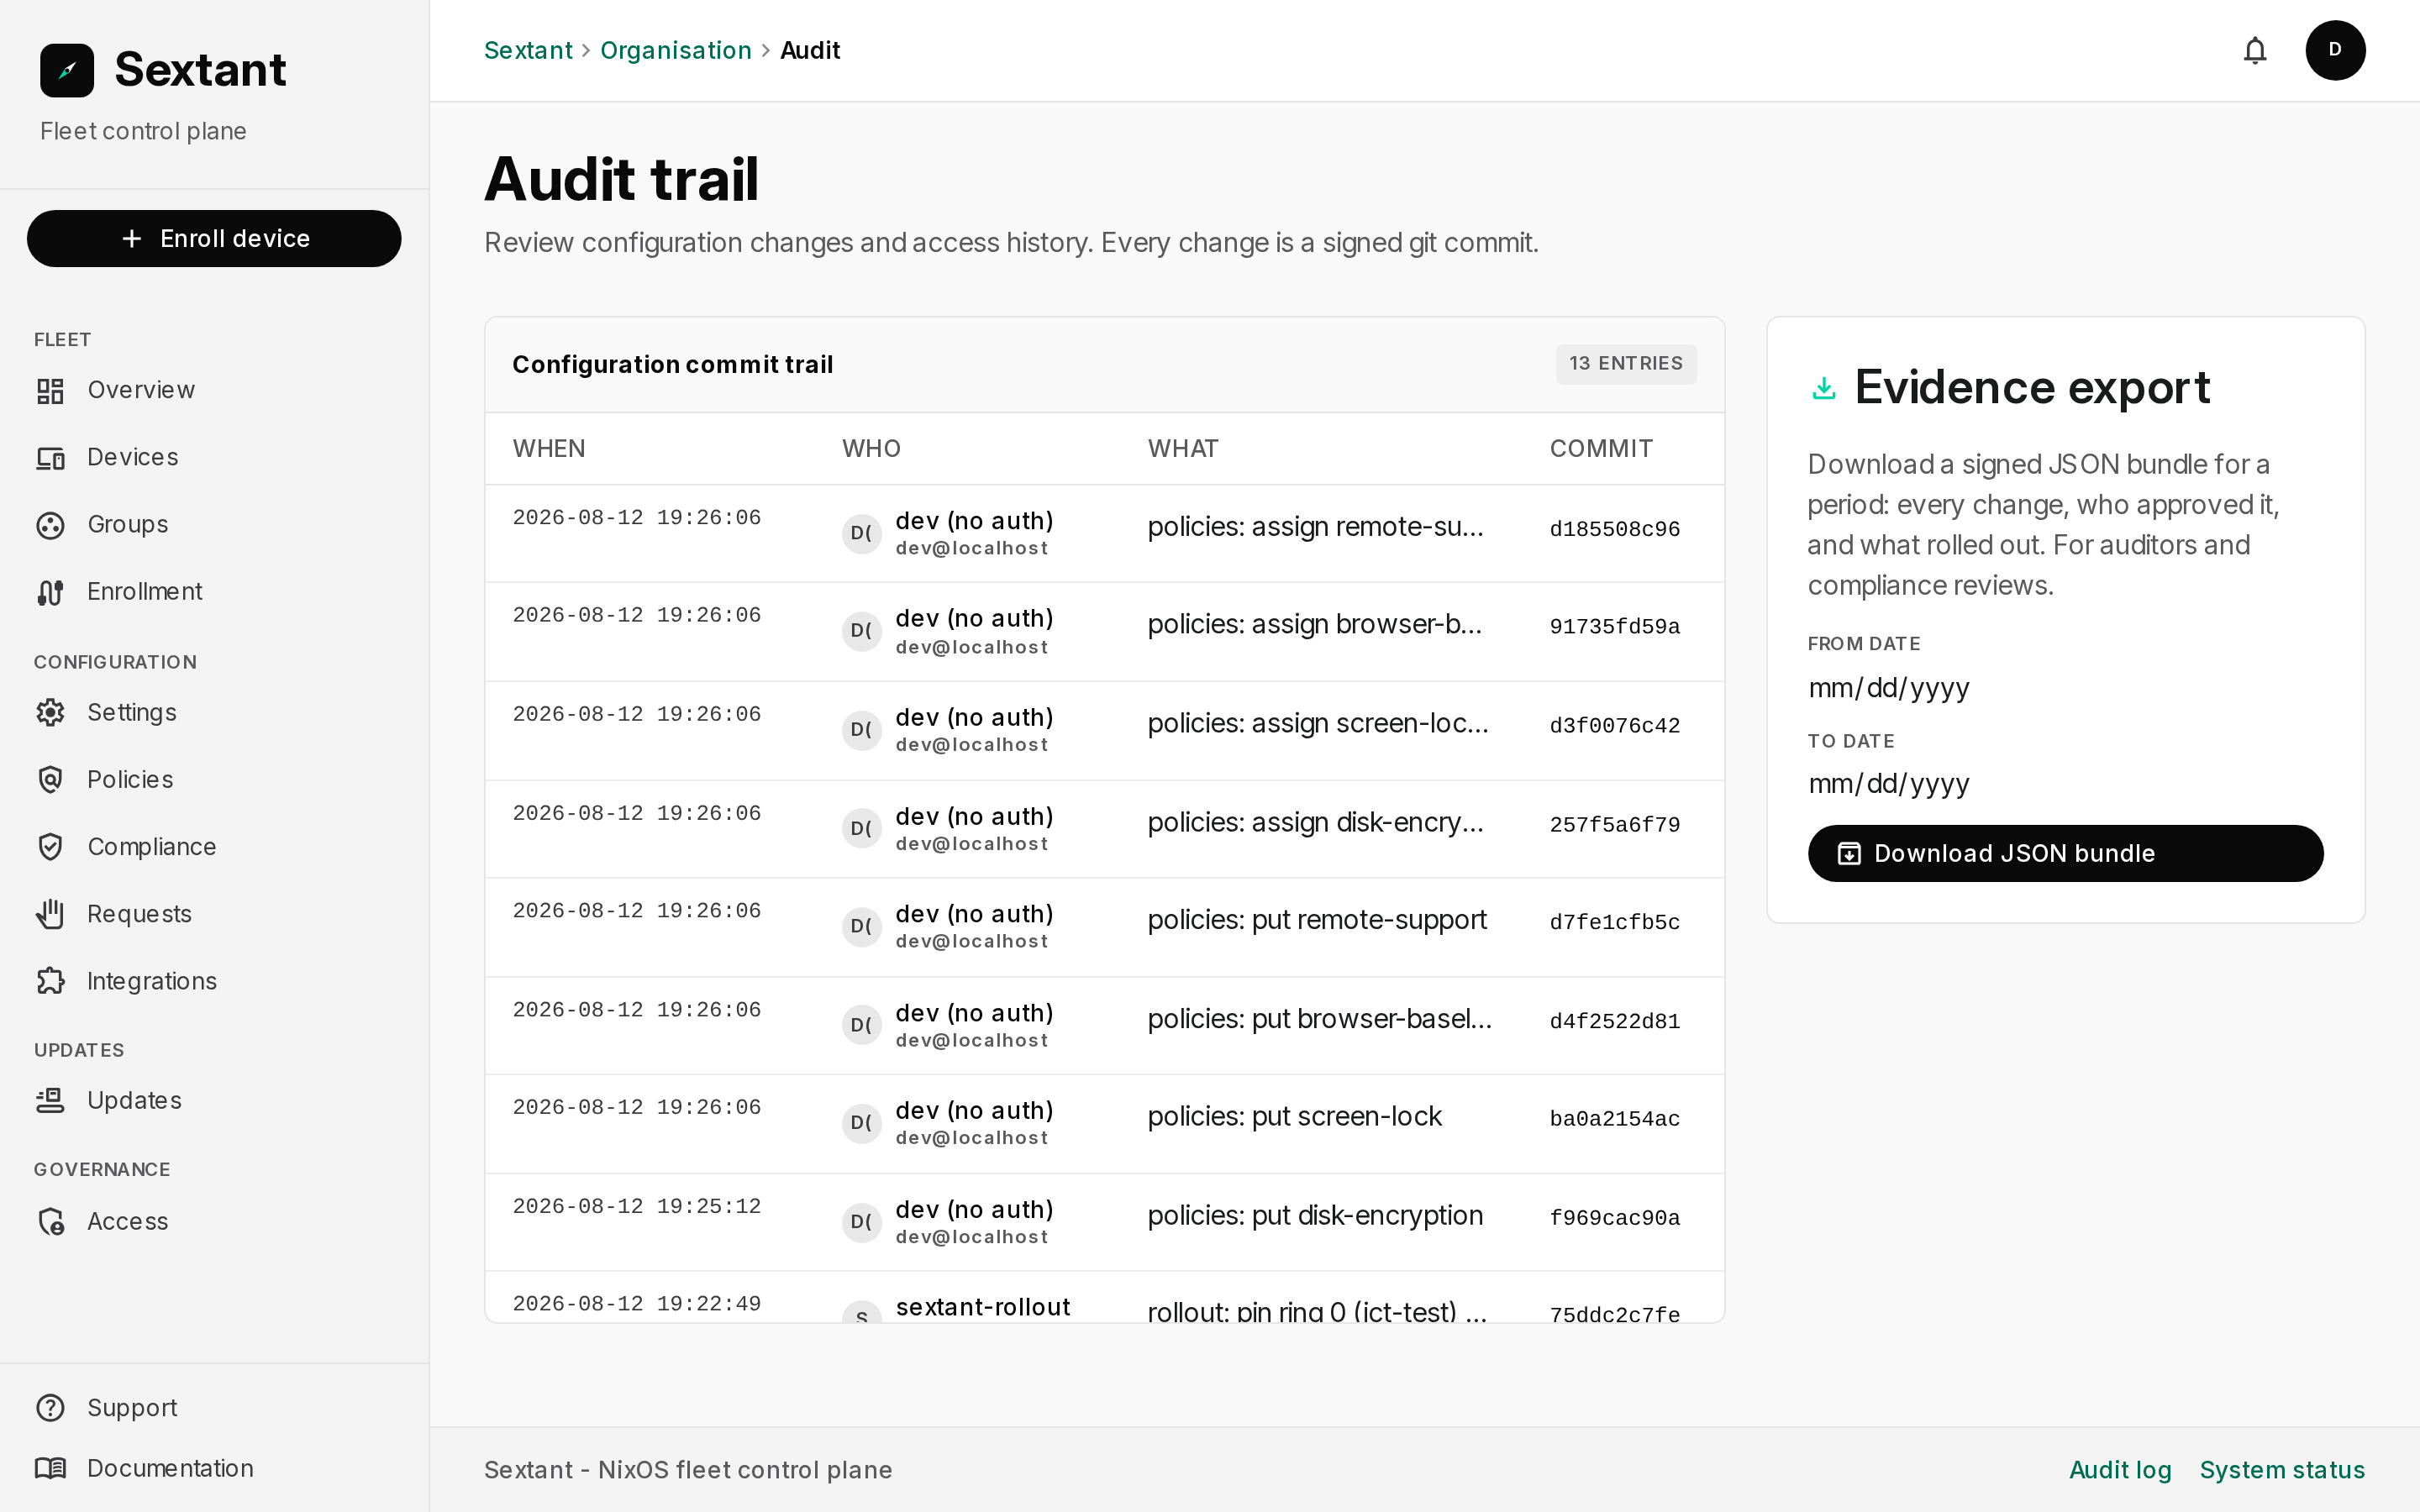
Every change is a signed commit.
Configuration changes land in your own git as commits with an author and a timestamp, whether they were made in the console or in the file. An evidence export for a period is a signed bundle: every change, who approved it, and what rolled out.
Mapped to the controls you are asked about.
Policies carry their control references, so an export is grouped the way an auditor reads it rather than the way the product happens to store it.
- ISO 27001
- ISO 27002
- NIS2
- National baselines such as the Dutch BIO
NIS2 moved the question from trust to proof.
Directors are personally accountable now. Sextant shows what is on a laptop, exactly, instead of a report about what should be on it.
A full list of what runs
Which software is on which laptop, down to the version.
Software you keep yourself
Your own copy of everything the fleet installs, so a hacked supplier does not reach you.
Evidence, not a report
ISO 27001 and NIS2 evidence, exported per control, straight from what the laptops report.
One document for every laptop.site.audit.
Take it, run it, help build it.
The software is yours under the EUPL 1.2 and needs nobody’s permission. What the project needs is people: a laptop model we have never imaged, a language nobody has translated, a bug found by running it for real.